Built by people who have had to use the alternatives.
Denwen RMM is made in the United Kingdom for managed service providers and internal IT teams. It exists because the tools in this category tend to be bought on a feature list and lived with on a Tuesday afternoon, and those are not the same document.
What we are trying to do
Make a platform an administrator can inspect rather than trust. Most of what an RMM does is invisible: it runs privileged code on machines nobody is sitting at, and reports back that it worked. The interesting question is never whether the feature exists — it is whether you can tell, afterwards, what actually happened.
So the product is built around evidence. Commands are signed and the agent proves it verified them. The audit trail is enforced by the database rather than by the application promising to write to it. The data-protection register reads the running system instead of repeating a document. Where something cannot be proven, it says so rather than showing a green tick.
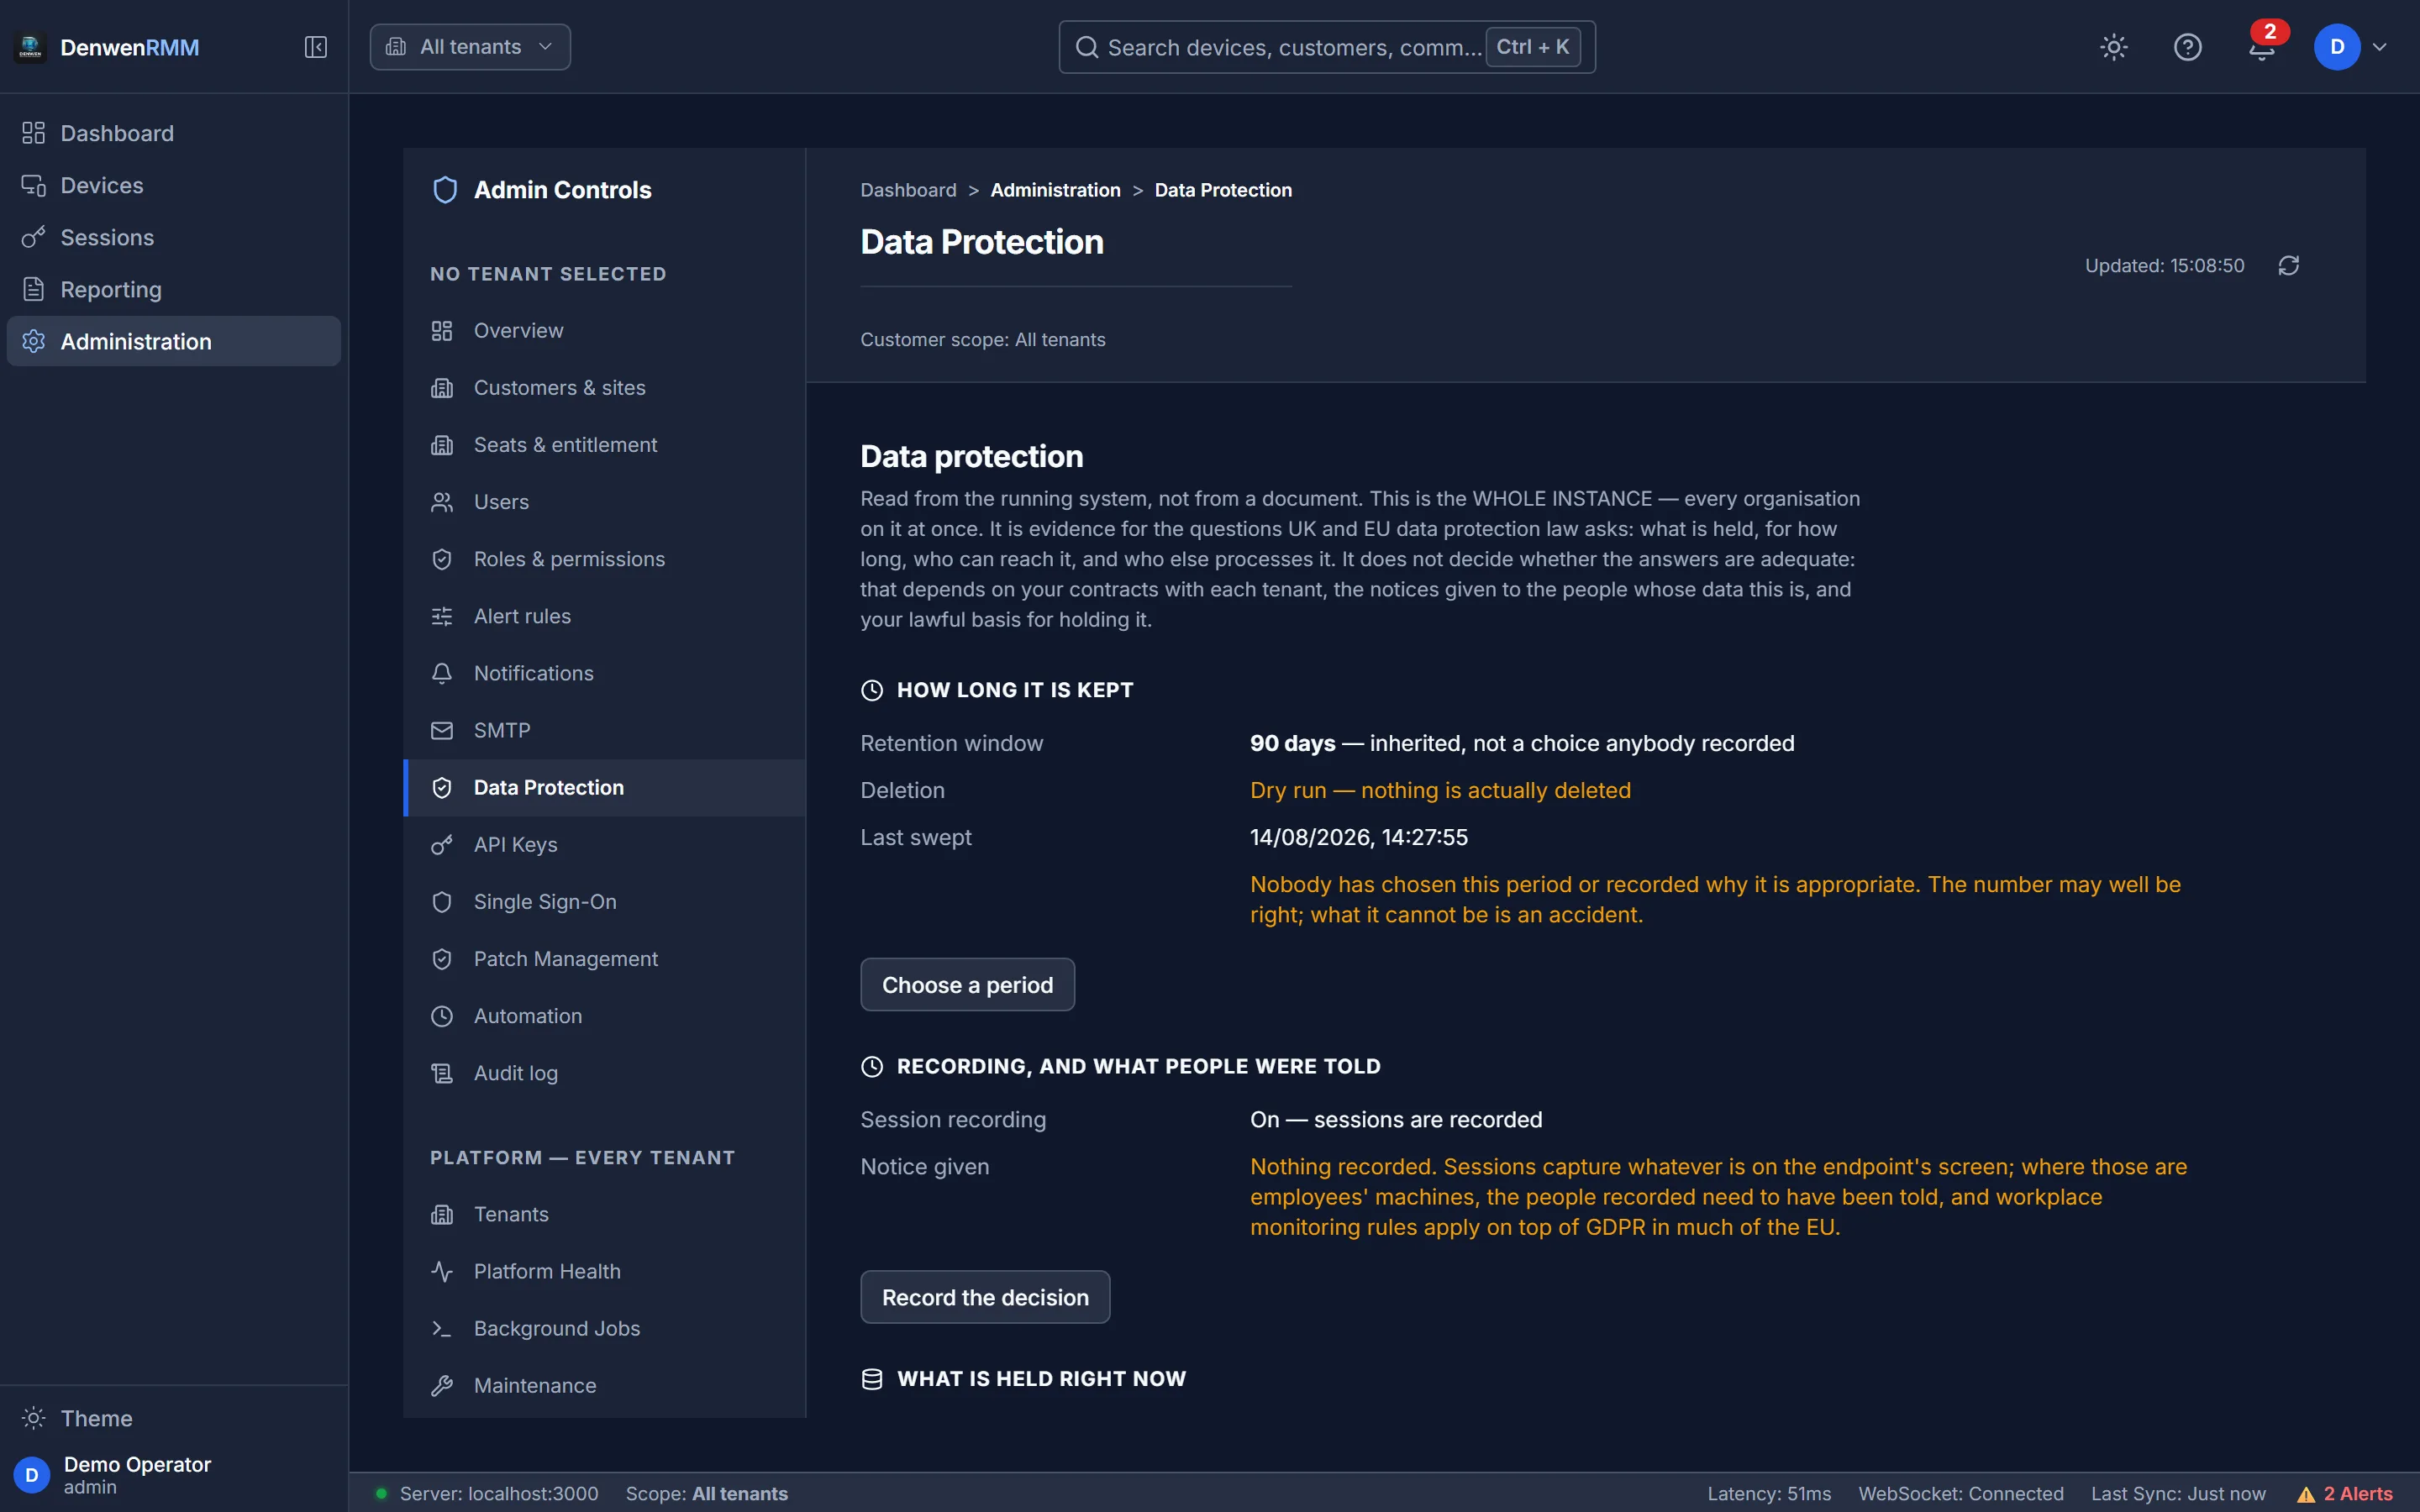
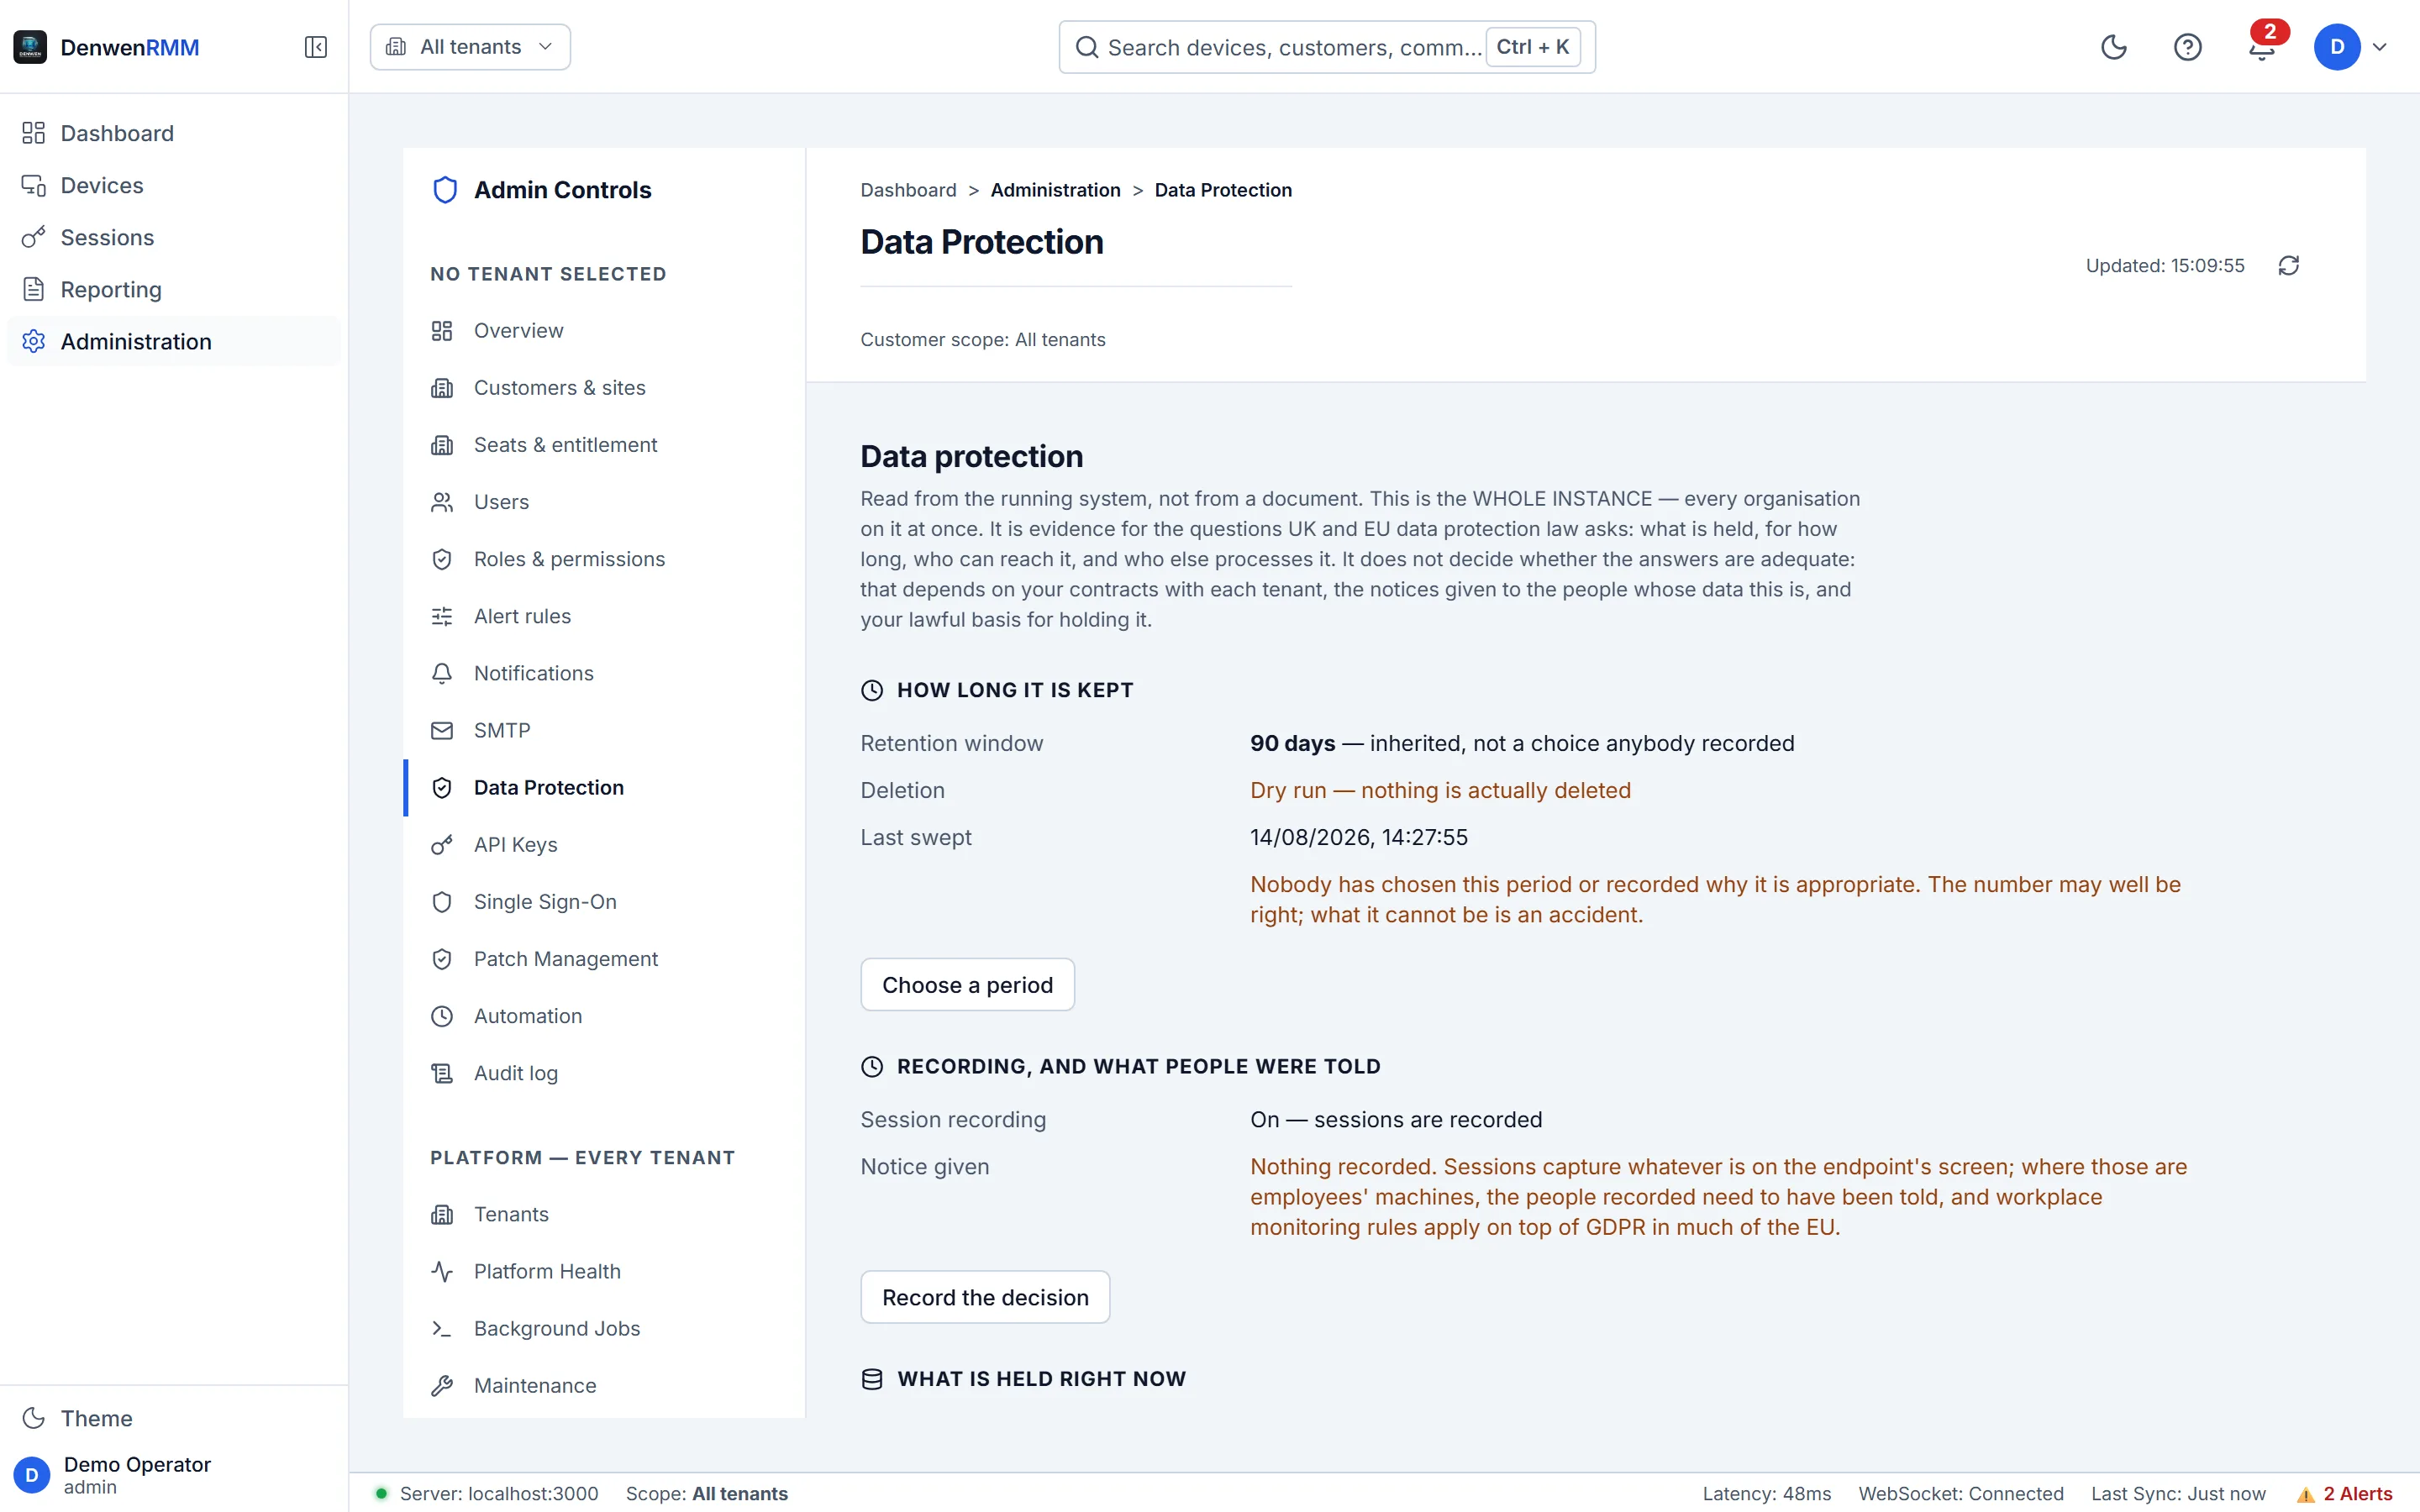
How that shows up in the build
- A build that fails on a design-token violation, a contrast failure or an unclassified form field
- A deployment tool that refuses when it cannot verify the signing key the server loaded
- An audit table the database will not let the application update or delete
- Tests written against the failure that happened, not the code that was written
Three commitments, all of them checkable.
The price is published
Including the volume bands. You should be able to price a bid on a Friday afternoon without booking a call with anybody.
The trial is on your machines
Not a sandbox with somebody else’s devices in it. Ten of your own endpoints tells you more than any demonstration.
You can leave
Your data exports, the schema is documented, and a lapsed subscription goes read-only rather than dark so you can get it out.
Talk to the people who build it.
No qualification form and no discovery call before a straight answer. If the answer is that we are not the right fit, you will get that too.
Get in touch
hello@denwen.co.uk for anything commercial or technical.
security@denwen.co.uk for a vulnerability report. We will acknowledge inside one working day and we will not threaten you.
Evaluating seriously?
Send the questions your security team or your client’s auditor is asking. We would rather answer them in writing before a trial than discover halfway through that the answer was going to be no.
See it on your own estate
A trial runs on your real endpoints, not a sandbox, and needs no payment details. Install the agent on ten machines and judge it on what it reports back.